Every device on your network, recorded down to the firmware.

A port scan tells you a device is there. Open-AudIT records what it is and every change since, and uses AI to match its software to known vulnerabilities.

See AI-powered vulnerability matching

Windows · Linux · VM with NMIS · free to download

Enterprise · free for your first 30 days. The full product and unlimited devices from day one. When the trial ends, Free keeps working on up to 100 devices.

Basic scanIllustrative
Host
200.159.233.1 is up
22/tcp
open ssh
161/udp
open snmp
443/tcp
open https

4 facts

Open-AudIT recordExample recordcisco-air-9DELKWMSY2O

Identity and hardware

Manufacturer
Cisco Systems
Model
AIR-CTVM-K9
Serial
9DELKWMSY2O
Type
Switch
Description
Cisco Controller

OS and firmware

OS Group
Cisco
OS Name
Cisco IOS-XE 8.7.106.0

Network

Where it lives

History

7 of 19 facts shown

The same device, two ways. Record values come from a real Open-AudIT device record.

FirstWave customers include

  • L3Harris Technologies
  • Raytheon
  • Pega
  • NASA
  • Telmex

AI-powered vulnerability matching, and the benchmarks your auditor will ask for.

Know which CVEs affect the software you actually run, and whether each machine is configured the way your auditor expects, before the audit.

AI-powered vulnerability matching Professional and Enterprise

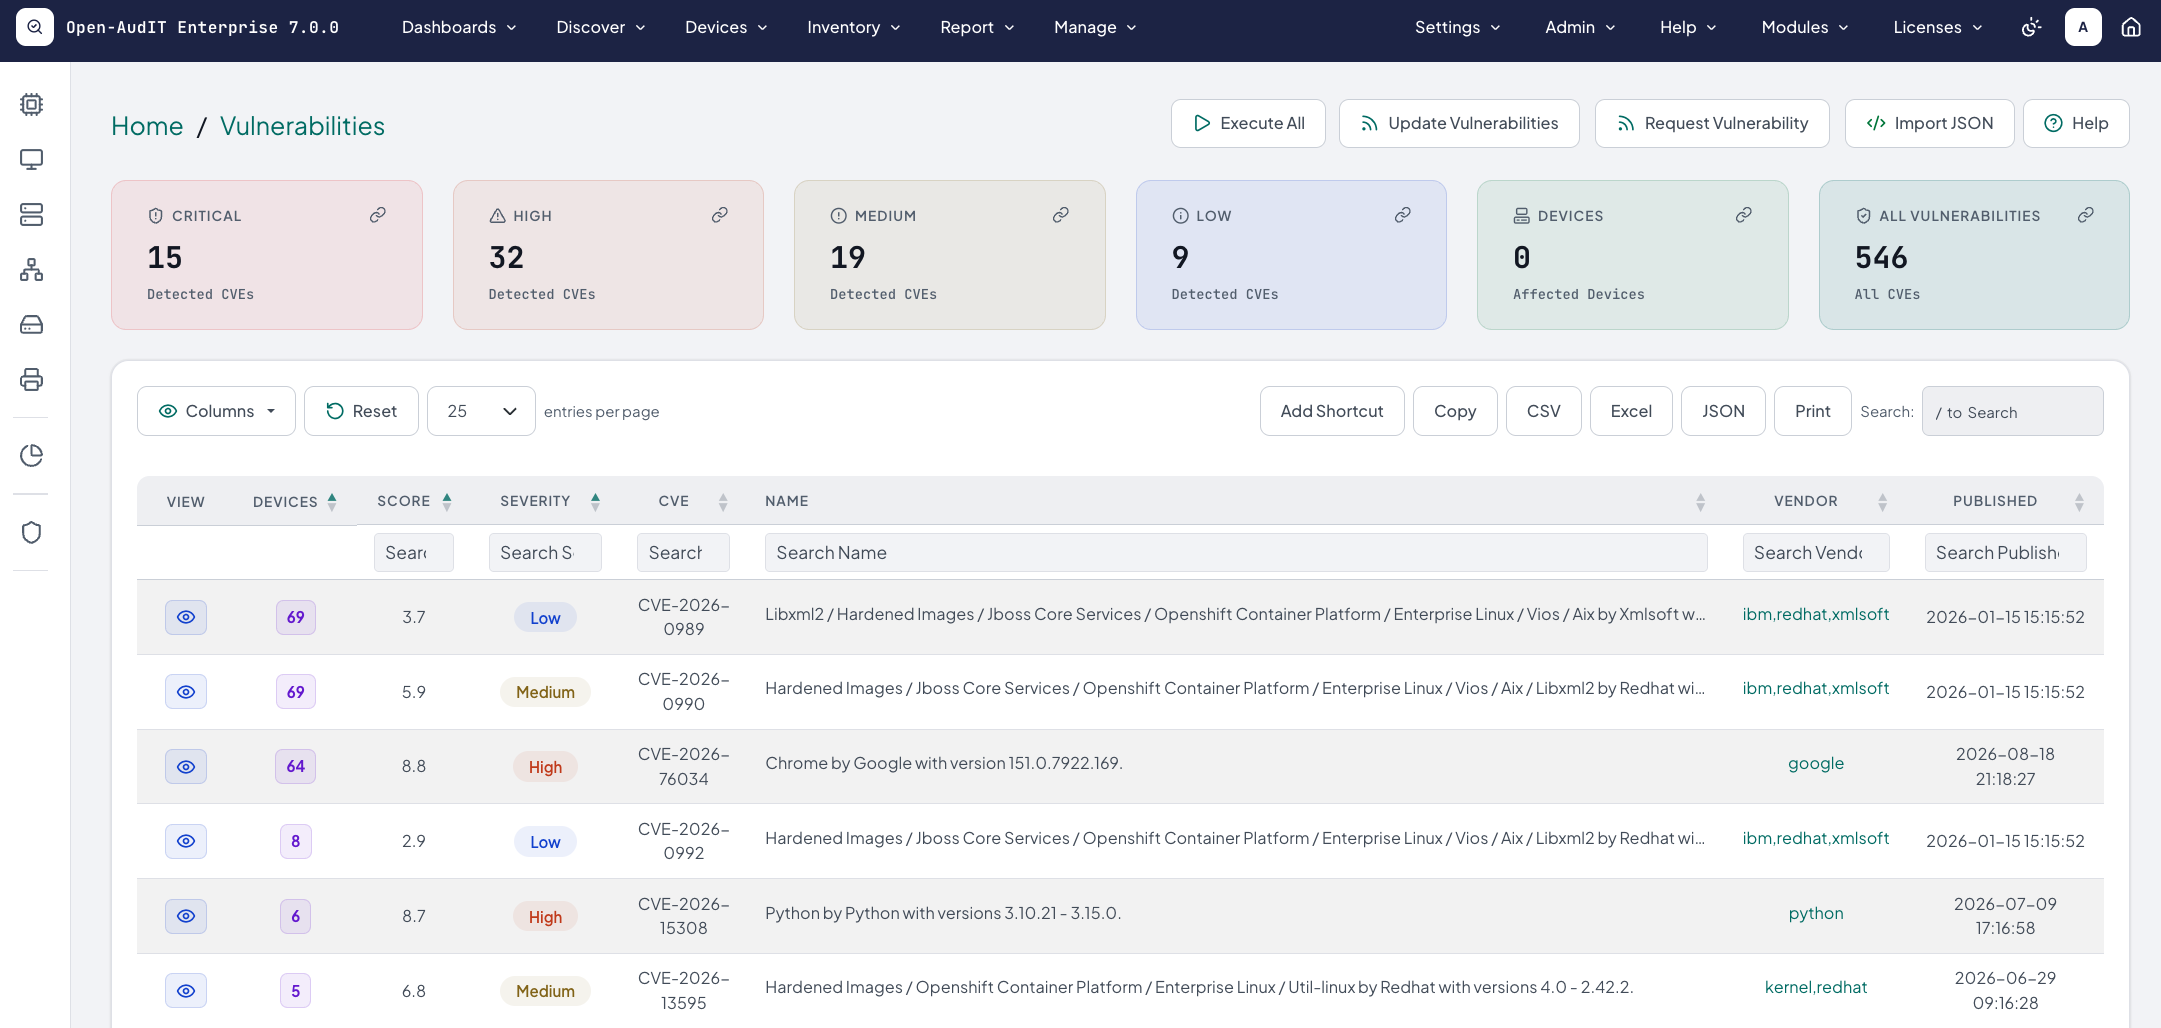
AI matches the software installed on each device to published CVEs and alerts you to the ones that affect you.

Matched to what you run
Only CVEs that apply to software found on your devices, not the whole feed.
Alerted on new risks
When a new CVE matches something you run, you hear about it.
Reported by device
Reports show each affected device and the risk severity.
Vulnerability detection in detail
Open-AudIT 7.0.0Vulnerabilities
Detected CVEs counted by severity, and each CVE listed with the number of devices it affects, its score, severity, vendor and publish date.

Benchmarks Enterprise

Each machine is checked against a published standard, every rule graded by severity and marked pass or fail.

Benchmarks in detail
Linux
CIS Benchmarks, DISA STIG, NIST 800-171, ACSC Essential Eight, ACSC ISM, HIPAA, PCI-DSS v4.0 and ANSSI.
Windows
DISA STIG checks run as part of a normal audit.
Active Directory
Benchmarked against the DISA STIGs.
Standards reporting
ISO 27001, CBDDO, BDDK, NCA ECC and ASD Essentials, 1,304 controls in all.

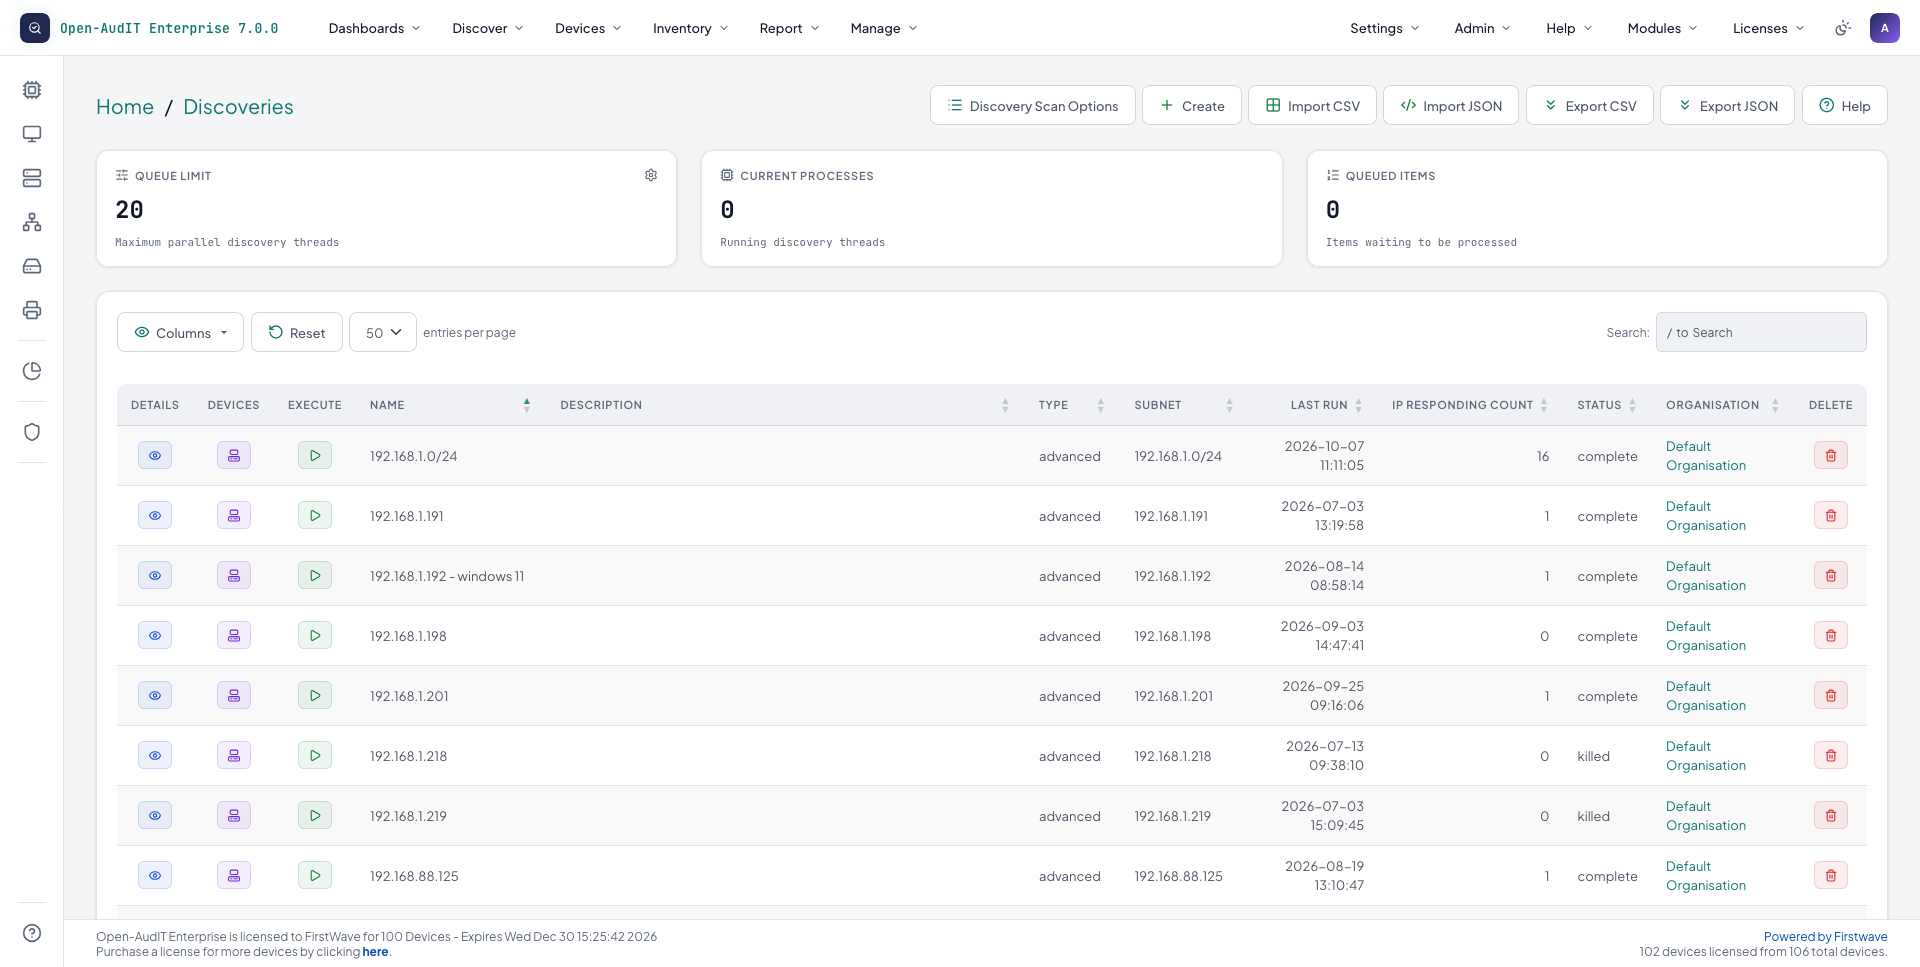
Open-AudIT 7 finds the devices nobody gave you a login for.

A new discovery engine identifies equipment from the protocols it already speaks, without needing a credential for most of it. Add credentials and it discovers even more. Open-AudIT 7 recognises 3.6 times as many device types as version 6.

Enterprise · free for your first 30 days. The full product and unlimited devices from day one.

Open-AudIT 7.0.0Discoveries
Every discovery with its subnet, last run, responding IP count and status, under the discovery queue.

One device, two depths

A basic scan returns four facts about this device. The record here shows nineteen of the fields Open-AudIT keeps, and every change is logged after that.

Basic scanIllustrative
Host
200.159.233.1 is up
22/tcp
open ssh
161/udp
open snmp
443/tcp
open https

4 facts

Open-AudIT recordExample recordcisco-air-9DELKWMSY2O

Identity and hardware

Manufacturer
Cisco Systems
Model
AIR-CTVM-K9
Serial
9DELKWMSY2O
Type
Switch
Description
Cisco Controller

OS and firmware

OS Group
Cisco
OS Name
Cisco IOS-XE 8.7.106.0

Network

IP
200.159.233.1
IP Addresses
3 recorded
SNMP Details
recorded

Where it lives

Organisation
Default Organisation
Status
Production
Environment
Production
Location
recorded
Purchase
recorded

History

Discovery Log
25 entries
Edit Log
38 entries
Change Log
1 entry
Audit Log
1 entry

19 of 19 facts shown

  1. Identity and hardware

    Manufacturer, model, serial and device type, read from the device itself rather than guessed from an open port.

  2. OS and firmware

    The OS family and exact version. On network gear like this controller, that version is the firmware release.

  3. Network

    Every IP address the device holds, plus the SNMP details it reports.

  4. Where it lives

    Organisation, status, environment, location and purchase details, so the record says who owns the device and where it sits.

  5. History

    Every discovery, edit and change is logged against the device, so you can see what changed and when.

How it collects

Open-AudIT talks to each device in the protocol it already speaks, so there is nothing to roll out first.

SNMP

Routers, switches, printers and other network gear

Reads make, model, serial, firmware and interfaces from the device's SNMP data.

WMI

Windows computers and servers

Collects hardware, installed software and configuration over WMI, using credentials you supply.

SSH

Linux, Unix, macOS and ESXi

Runs audit commands over SSH to collect hardware, packages and configuration.

Agent

Machines discovery cannot reach

For air-gapped or restricted sites, Open-AudIT also supports agent-based audit.

What teams actually use Open-AudIT to do

  • Pass the next audit without the all-hands fire drill.

    Generate inventory, configuration, and compliance evidence on demand against NIST, ISO 27001, Essential Eight, and CIS Controls. The data is already there because Open-AudIT has been collecting it.

    Learn more
  • Find the assets nobody told you about.

    Continuous discovery surfaces unauthorised devices, shadow IT, and end-of-support hardware before they show up in an incident report.

    Learn more
  • Catch configuration drift before it becomes an outage.

    Track every configuration change across servers, network gear, and endpoints. Get alerted when something drifts from the expected baseline.

    Learn more
  • Prioritise the vulnerabilities that actually matter.

    Open-AudIT matches installed software to CVEs with AI and alerts you, so the team is not chasing CVEs that do not affect you.

    Learn more

Every device in one searchable list

Discovery results land in one table you can search, filter, export to CSV or Excel, and open device by device.

Open-AudIT device list showing discovered devices with type, IP address, operating system, manufacturer and description
Open-AudIT · DevicesSwipe to see the full tableDevices found by a discovery run

Open source from the first release

Open-AudIT started as an open source project and the source code, documentation, and roadmap remain freely available. Commercial subscriptions add automated benchmarking, vulnerability detection with AI CVE matching, and enterprise support.

Buy Open-AudIT on AWS Marketplace

If you're standardising procurement through AWS, you can purchase Open-AudIT directly on AWS Marketplace. Deploy in AWS or on-prem, align spend to your AWS commitments, and get started faster.

See what is really on your network.

Download Open-AudIT, point it at a subnet and read the records it builds. Free to download, and it installs on your own server.

Enterprise · free for your first 30 days. The full product and unlimited devices from day one. When the trial ends, Free keeps working on up to 100 devices.